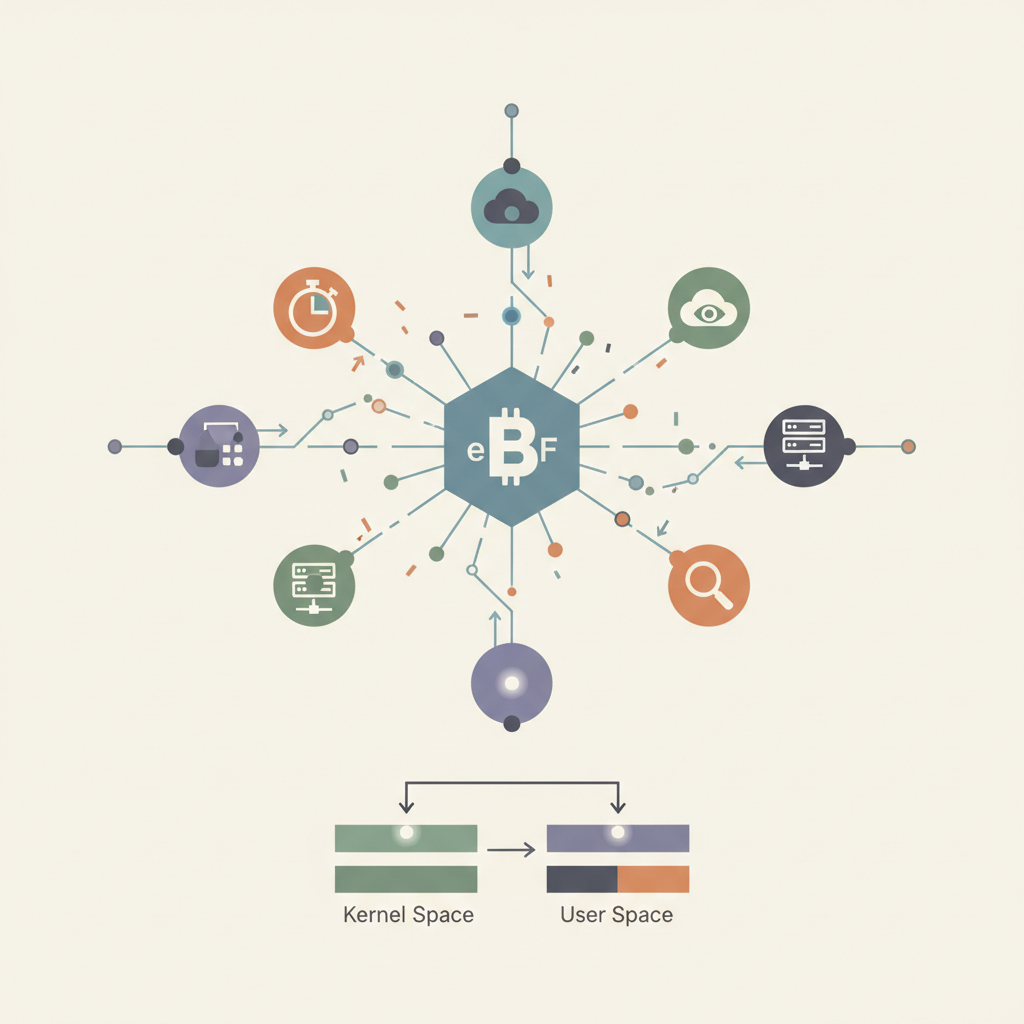
Diagram of the eBPF verifier, JIT, and hook points inside the Linux kernel.

Inside eBPF: How the Linux Kernel Runs Sandboxed Programs Inside Itself

TL;DR — eBPF lets you load and run sandboxed bytecode inside the Linux kernel at near-native speed, attached to hooks like network events, syscalls, and tracepoints. A static verifier guarantees the program terminates and stays safe before a JIT compiler turns it into machine code, which is why tools like Cilium, Pixie, and bpftrace have reshaped observability and networking in production. If you’ve shipped a service on Linux in the last five years, you’ve almost certainly been touched by eBPF — even if you never wrote a program yourself. Cilium powers the networking and service mesh layer for hyperscalers like AWS and Shopify. Datadog and New Relic ship kernel probes for zero-instrumentation tracing. Cloudflare uses eBPF to do connection tracking and DDoS mitigation at line rate. The reason this is possible is a piece of kernel machinery that turns “the kernel is a closed black box” into “the kernel is a programmable, observable, auditable system,” without compromising its stability. ...
September 4, 2026 · 12 min · 2362 words · martinuke0
Network packets flowing through an eBPF/XDP datapath diagram.

Building an eBPF-Powered Packet Classifier in C: A CV-Worthy Systems Project

Build a production-shaped eBPF/XDP packet classifier from scratch in C. Real code, real architecture, and a clear roadmap to extend it into a senior-level systems project.

September 3, 2026 · 11 min · 2172 words · martinuke0
Network diagram showing multiple Kubernetes clusters connected through an Istio ambient mesh with ztunnel and waypoint components.

Architecting Multi-Cluster Service Mesh with Istio Ambient Mode and eBPF

A practical architecture guide to running Istio Ambient Mode across multiple Kubernetes clusters, with eBPF-powered data planes handling L4 and waypoint proxies owning L7.

September 3, 2026 · 12 min · 2493 words · martinuke0
Short description of the cover image subject.

Implementing eBPF for Production Observability: A Deep Dive into High-Performance System Tracing and Monitoring

A practical guide to integrating eBPF into production observability stacks, with architecture diagrams, code snippets, and lessons from large‑scale deployments.

June 2, 2026 · 7 min · 1488 words · martinuke0
A Linux kernel symbol table overlaid with a glowing eBPF map.

Implementing eBPF for Tracing and Production Observability: Architecture, Performance, and Real-World Patterns

A deep dive into eBPF‑based tracing, showing how to design a production‑grade observability stack, measure its impact, and apply battle‑tested patterns.

June 1, 2026 · 7 min · 1301 words · martinuke0
Feedback